Exoscale Installation
Plakar Control Plane is distributed for Exoscale as a QCOW2 virtual machine image. The official QCOW2 image can be downloaded from:
Unlike marketplace-based deployments such as AWS AMIs, Exoscale instances cannot boot directly from a QCOW2 image. Instead, the image must first be registered as a Compute custom template, which can then be used to create instances.
Preparing the QCOW2 image
Exoscale needs a publicly accessible URL to download the QCOW2 image from when creating the custom template, along with its MD5 checksum to verify the image during import. There are two ways to provide the URL:
- Direct download (recommended): use the download link from the downloads page directly as the image source. No re-hosting is required.
- Self-hosted: re-upload the QCOW2 image to your own publicly accessible
storage, such as Exoscale’s Simple Object Storage (SOS). Use this if you want
to keep your own copy of the image, or if your environment can’t reach
plakar.iodirectly when creating the template.
The downloads page publishes a SHA-256 checksum, but Exoscale only accepts
MD5. Whichever option you choose, download the image locally, confirm that its
SHA-256 checksum matches the one on the downloads page, then generate its
MD5 checksum:
sha256sum plakar-appliance-<version>.qcow2
md5sum plakar-appliance-<version>.qcow2
QCOW2 Image URL
Whichever option you choose, the image URL must be publicly accessible. Exoscale downloads the image directly when creating the custom template, so the URL cannot require authentication.
Hosting the QCOW2 image with Exoscale Simple Object Storage
This step is only needed if you’re following the self-hosted option above. If you’re linking directly to the downloads page, skip ahead to Creating the custom template.
Open the Storage section in the Exoscale console and create a new Simple Object Storage (SOS) bucket. Choose a zone for the bucket and provide a name. The region does not matter for this purpose.
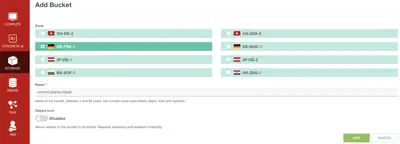
Once the bucket has been created, open it and click Upload object. Upload the QCOW2 image that you downloaded earlier.
After the upload completes, open the uploaded object and navigate to the ACL tab. Click ADD CANNED ACL, then select PUBLIC-READ. This makes the object publicly accessible so Exoscale can download it when creating the custom template.
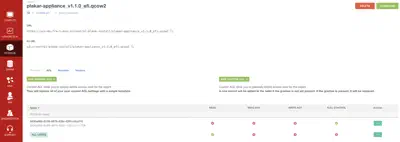
You can then copy the object’s URL and use it when registering the custom template in Exoscale.
Creating the custom template
Open Compute → Templates in the Exoscale console, then click Add custom template.
Provide a name for the template and select the zone where it will be created. The template can only be used to create instances in the same zone, so choose the zone where you intend to deploy Plakar Control Plane.
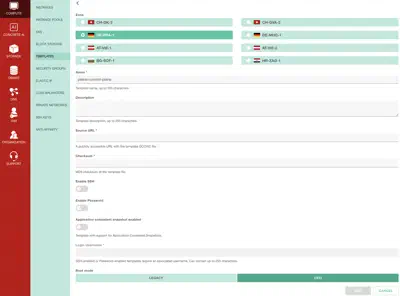
For the image source, provide the public URL of the QCOW2 image, either the
direct download link from the downloads page or your SOS object URL, then enter
the MD5 checksum you generated. Set the boot mode to UEFI.
If you intend to use Exoscale’s Application Consistent Snapshots, enable Application consistent snapshot when creating the custom template. This option cannot be enabled later unless it is supported by the template.
If you want SSH access to the instance, enable SSH access and set the
Login username to plakar. SSH access is optional and is not required for a
standard installation. Plakar Control Plane is designed to be managed through
the web interface.
Once the template has been configured, click Add to create the template.
SSH Access
SSH-enabled templates require a public SSH key. If SSH access is enabled, you’ll be able to connect to the instance after deployment using:
ssh plakar@<instance-ip-address>Replace <instance-ip-address> with the public IP address assigned to the
instance.
Creating the instance
Open Compute → Instances in the Exoscale console, then click Add instance.
Provide a name for the instance. Under Templates, select Custom template, then choose the template created in the previous step.
Once a custom template has been selected, the instance is automatically created in the same zone as the template. The zone cannot be changed, so ensure the template was created in the zone where you intend to deploy Plakar Control Plane.
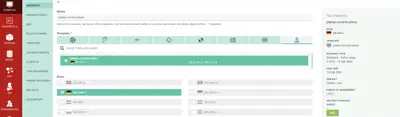
Size the instance according to Appliance Sizing, which gives the CPU, memory and disks for each size of deployment. For the S tier, an Extra Large instance from the Standard instance type family is suitable. The template only requires a small system disk. Plakar Control Plane stores its database, logs, and application state on a separate Block Storage volume, which will be attached later.
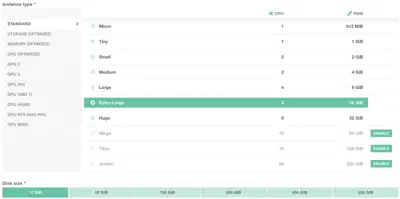
Configure the remaining instance options as needed for your environment.
To route outbound traffic through a proxy, or to change any other appliance setting, add it to the user data as described in Configuring the Appliance.
If SSH access was enabled when creating the custom template, select the SSH key pair to authorize for the instance.
Leave Public IP Assignment enabled so the instance receives a public IPv4 address that can be used to access Plakar Control Plane after deployment. If you’re deploying Plakar Control Plane behind a private network, you can disable public IP assignment instead.
You can also assign one or more Security Groups to the instance. This can be configured now or after the instance has been created. The recommended security group configuration is covered in the Security Groups section.
If the custom template was created with Application consistent snapshot support enabled, you can also enable it for the instance. This is optional and only required if you intend to use Exoscale’s application-consistent snapshot feature.
Before creating the instance, disable Auto start. This allows you to attach the additional Block Storage volume before Plakar Control Plane boots for the first time.
Once configured, click Create instance.
Creating the Block Storage volume
Open Compute → Block Storage in the Exoscale console, then click Create Block Storage.
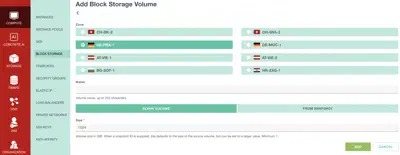
Provide a name for the volume, select the same zone as the instance, and create it as a Blank volume, of the data disk size given in Appliance Sizing.
Block Storage volumes can only be attached to instances in the same zone. This volume stores the Plakar Control Plane database, logs, and all application state. Backups themselves are stored wherever you configure using apps.
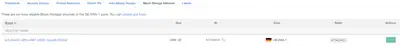
Once the volume has been created, open Compute → Instances and select the Plakar Control Plane instance. Under Block Storage Volumes, click Attach volume, then select the Block Storage volume that you created.
Configuring the Appliance
An instance with direct internet access needs no configuration, and SSH access comes from the key pair selected when creating the instance, if SSH access was enabled on the custom template. For anything else, such as a proxy or registry mirrors, the appliance reads its settings from the instance’s User data, set before the instance is created. The keys of the document are described in Appliance Configuration.
If the appliance goes through a proxy or firewall, the hosts it has to reach are listed in required outbound access.
The document below sets every key. Remove the ones your environment does not need, each key is optional.
#cloud-config
ssh_authorized_keys:
  - ssh-ed25519 AAAA...

proxy:
  http: http://proxy.corp.example:3128
  https: http://proxy.corp.example:3128
  no_proxy: .corp.example

registry:
  mirrors:
    docker.io: harbor.corp.example/dockerhub-proxy
    ghcr.io: harbor.corp.example/ghcr-proxy
  insecure: false

releases:
  url: https://dist.corp.example/plakar/enterprise
  version: v1.1.2

ntp:
  servers:
    - 10.20.0.1
    - ntp.corp.example

network:
  ethernets:
    eth0:
      addresses: [10.0.1.5/24]
      gateway4: 10.0.1.1
      nameservers:
        addresses: [10.0.1.53]
Security Groups
The networking configuration below is intended for a basic deployment setup.
In production environments, networking and access control should be adapted to match your infrastructure and security requirements. For example:
- Exposing Plakar Control Plane through a load balancer with HTTPS/TLS certificates
- Restricting access through a VPN or private network
- Limiting inbound traffic to trusted IP ranges
- Using internal-only networking
Create a security group that allows inbound TCP traffic on port 80 to access
the Plakar Control Plane web interface. If SSH access was enabled when creating
the custom template, also allow inbound TCP traffic on port 22.
The allowed source can be:
- Your public IP address
- Your organization gateway or VPN address
0.0.0.0/0for temporary testing access
By default, Exoscale allows all outbound traffic, so no additional egress rules are required.
Once the security group has been created, open the Plakar Control Plane instance and navigate to the Security Groups tab. Attach the security group to the instance.
Warning
Using 0.0.0.0/0 allows access from any IP address and should only be used
for testing or temporary deployments.
Starting the instance
After the Block Storage volume has been attached, start the instance from the Exoscale console.
Plakar Control Plane will detect and initialize the attached Block Storage volume during its first boot.
Accessing Plakar Control Plane
Once the instance has started with its Block Storage volume attached, Plakar
Control Plane is reached from a browser at http://<public-ipv4-address>, the
public IPv4 address of the instance, provided its security group allows inbound
traffic on port 80. For first-time installations, you will be guided through
the enrollment process to:
- Register the instance with Plakar services for licensing and billing
- Create the initial administrator account
See the enrollment documentation for more details.